Static and dynamic analysis of an ARM64 ELF sample from the Mirai/Gafgyt family.
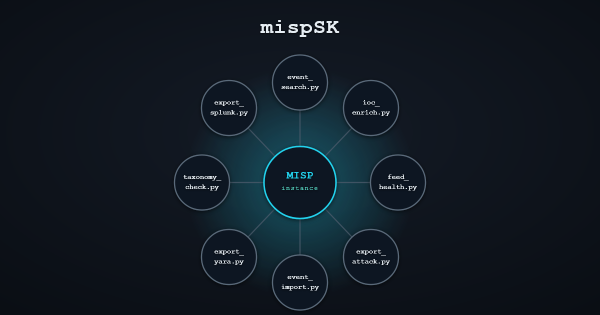
Collection of Python scripts automating operations on MISP instances through PyMISP.
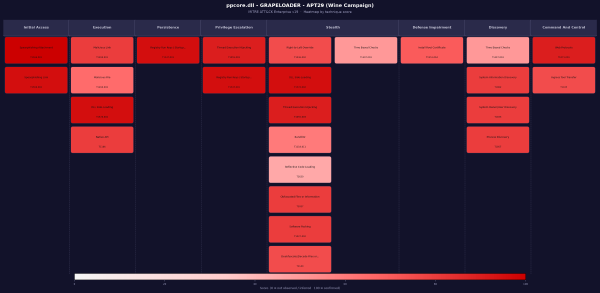
CLI tool that generates MITRE ATT&CK heatmaps from ATT&CK Navigator JSON layers.
Discord bot for static file triage and analysis.
Ghidra script framework for automated static detection of malware behaviors: anti-debug, anti-VM, packing, C2 indicators, process injection, persistence and defense impairment.
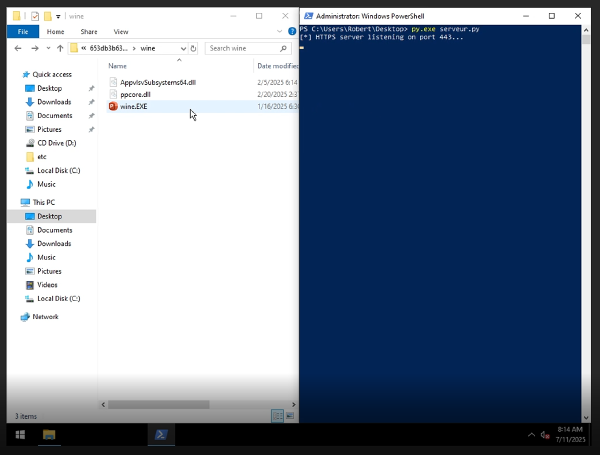
Analysis of the WINE malware attributed to APT29 in 2025, including a proof of concept.