Static and dynamic analysis of an ARM64 ELF sample from the Mirai/Gafgyt family.
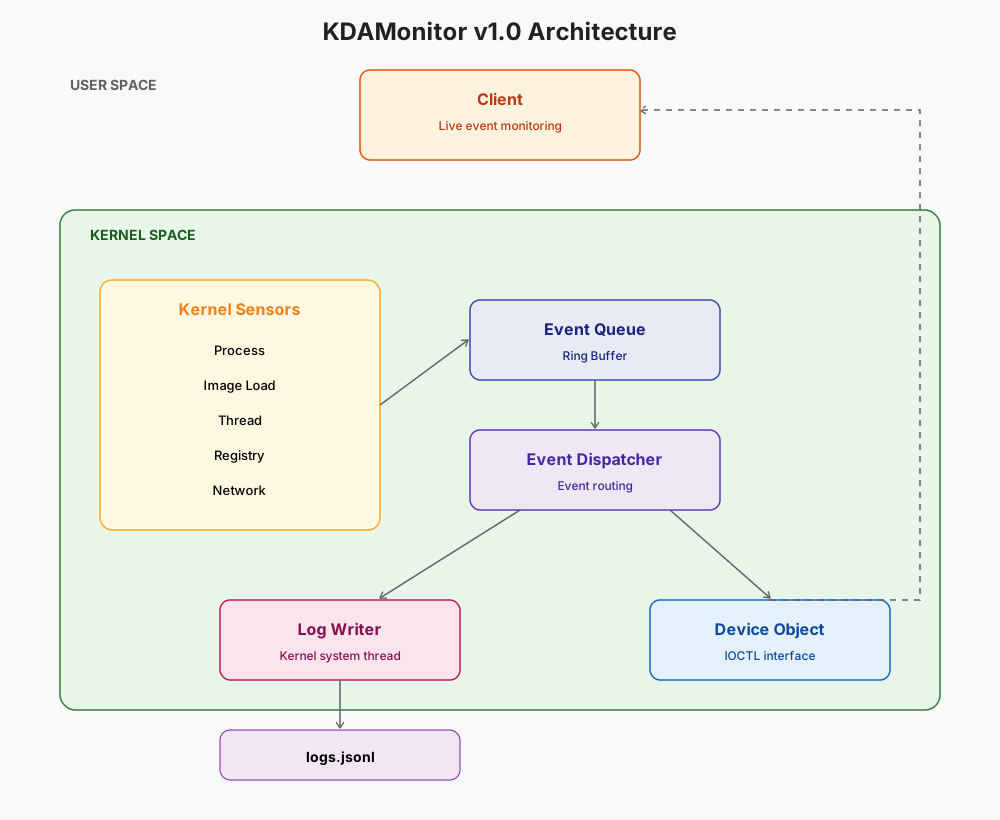
Windows kernel driver for malware analysis, logging process, image load, network, and registry activity in real time.
Discord bot for static file triage and analysis.
Ghidra script framework for automated static detection of malware behaviors: anti-debug, anti-VM, packing, C2 indicators, process injection, persistence and defense impairment.
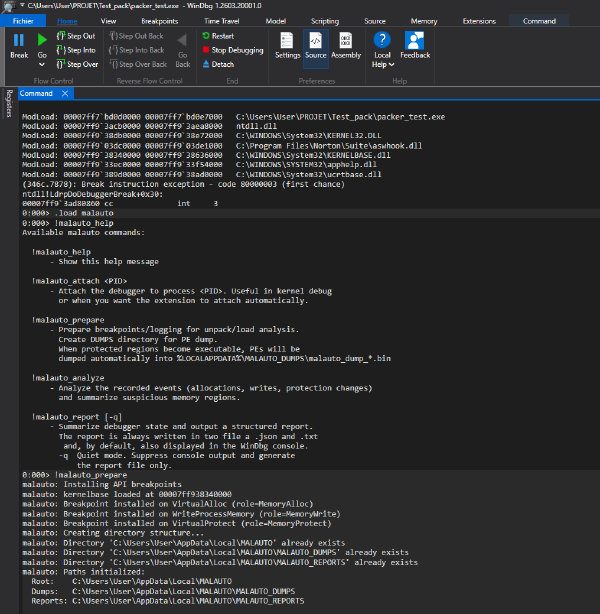
WinDbg extension for automated Windows malware analysis. Sets breakpoints, dumps memory regions in PE format and generates structured reports.
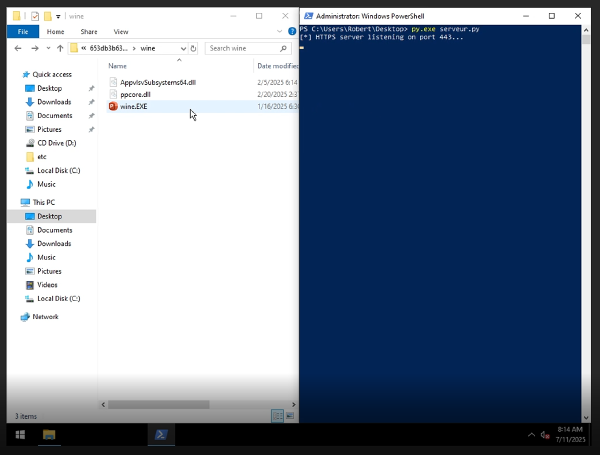
Analysis of the WINE malware attributed to APT29 in 2025, including a proof of concept.